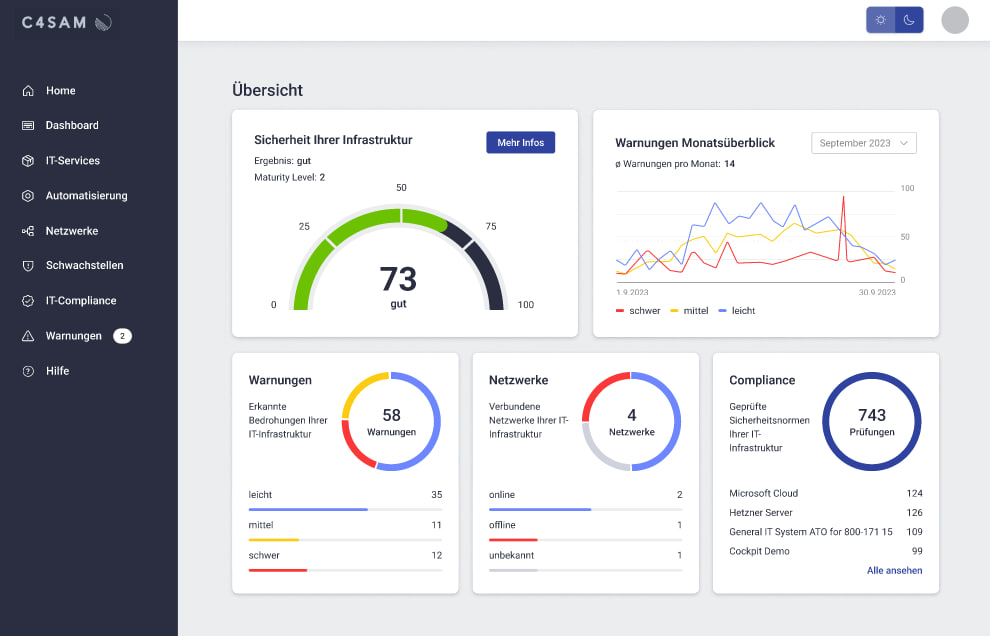
C4SAM consolidates findings from your existing tools and prioritizes them based on risk — with business context, not just CVSS. Your tools stay, the overview is added.
Tenable, CrowdStrike, Defender, your SIEM, Lansweeper — each delivers findings in its own format, in its own place. Consolidating them is manual work, often taking an entire person-day. Prioritization remains pure scanner severity without zone or business context. The result: misprioritization, blind spots in sensitive areas, and findings disappearing into black holes.
C4SAM connects the findings of all your sources into a consolidated, deduplicated picture. Each finding receives an explainable risk score (P1–P5) combining threat evidence, exposure, business impact, and technical impact — including the reason codes that triggered it. A flat list of 'critical' findings becomes a defensible, accountably assigned sequence.
All scanners in one view, with asset IDs normalized and deduplicated.
Business context and exposure flow into the decision — not just the CVSS number.
Bidirectional ticketing integration, status feedback, and re-scan verification.
Your scanners, your SIEM, and your SOC stay — C4SAM adds the missing layer in between.
Evidence and control mapping for frameworks such as NIS2, ISO 27001, GDPR, and DORA.
Full data control, GDPR-compliant, no vendor lock-in.
Start low-risk with two data sources and clear success criteria.
In a short demo, we demonstrate True Risk Priority on one of your use cases — from the consolidated view to assigned remediation.